A suspected ShinyHunters member has reportedly been detained in Jordan and is cooperating with the FBI after the hacking group claimed to have stolen highly sensitive information covering virtually the bureau’s entire workforce.
The suspect has been identified as Saif al-Din Khader, allegedly known in hacking circles as “Rey”. Jordanian authorities reportedly took him into custody on Tuesday, although the circumstances of his detention, his present location and any possible extradition request remain undisclosed.
Three people familiar with the investigation confirmed the detention. Two said Khader was helping the FBI and other international agencies identify additional members of the group. He is reportedly walking investigators through his electronic devices and digital communications, potentially exposing aliases, infrastructure and relationships used by the hackers.
I dont remember where I grabbed this but it was probably one of the 67 stealer infections on @dulls computer Dropbox ID for "0x rey" and Microsoft ID for "saif o5tswe" SLSH tries to deny it but Rey is 100% Saif Al-Din Khader Still waiting on that 10BTC bounty https://t.co/IsCixq7MMr
— IntelOps (@IntelOpsV3) November 30, 2025
Neither the FBI nor Jordan has publicly confirmed the detention. The bureau said it was continuing to investigate the cyber incident allegedly involving ShinyHunters and had already worked with international partners to arrest multiple suspects.
ShinyHunters claimed in September that it had compromised the FBI’s online recruitment system and stolen between two and three terabytes of information. The group said the material covered serving and former employees as well as people who had applied for positions.
The FBI confirmed that its jobs portal had been compromised, but said investigators had not established whether the entry point was an internal bureau system or technology operated by a third-party provider.
A sample released by the hackers reportedly contained Social Security numbers, addresses, assignments, names of family members and employment information. Other files included psychiatric assessments, prescriptions, medical records and “fitness for duty” examinations.
The FBI has not verified the group’s claim that almost every employee was affected. However, an internal bureau memorandum reportedly instructed personnel to operate on the assumption that the entire workforce had been exposed.
The stolen material could be valuable to identity thieves, criminal groups and foreign intelligence services. Medical conditions, family information and classified job roles could potentially be used for surveillance, coercion or efforts to identify undercover personnel.
The breach highlights the danger created when recruitment portals and outside service providers hold information connected to national-security institutions. India recently confronted a different verification failure after investigators uncovered credentials for more than half a million allegedly fraudulent Gmail accounts.
Khader’s detention follows the arrest of suspected ShinyHunters figure Pepijn van der Stap in the Netherlands. The FBI said the network had breached more than 140 organisations since 2025 and received at least $70 million in extortion payments.
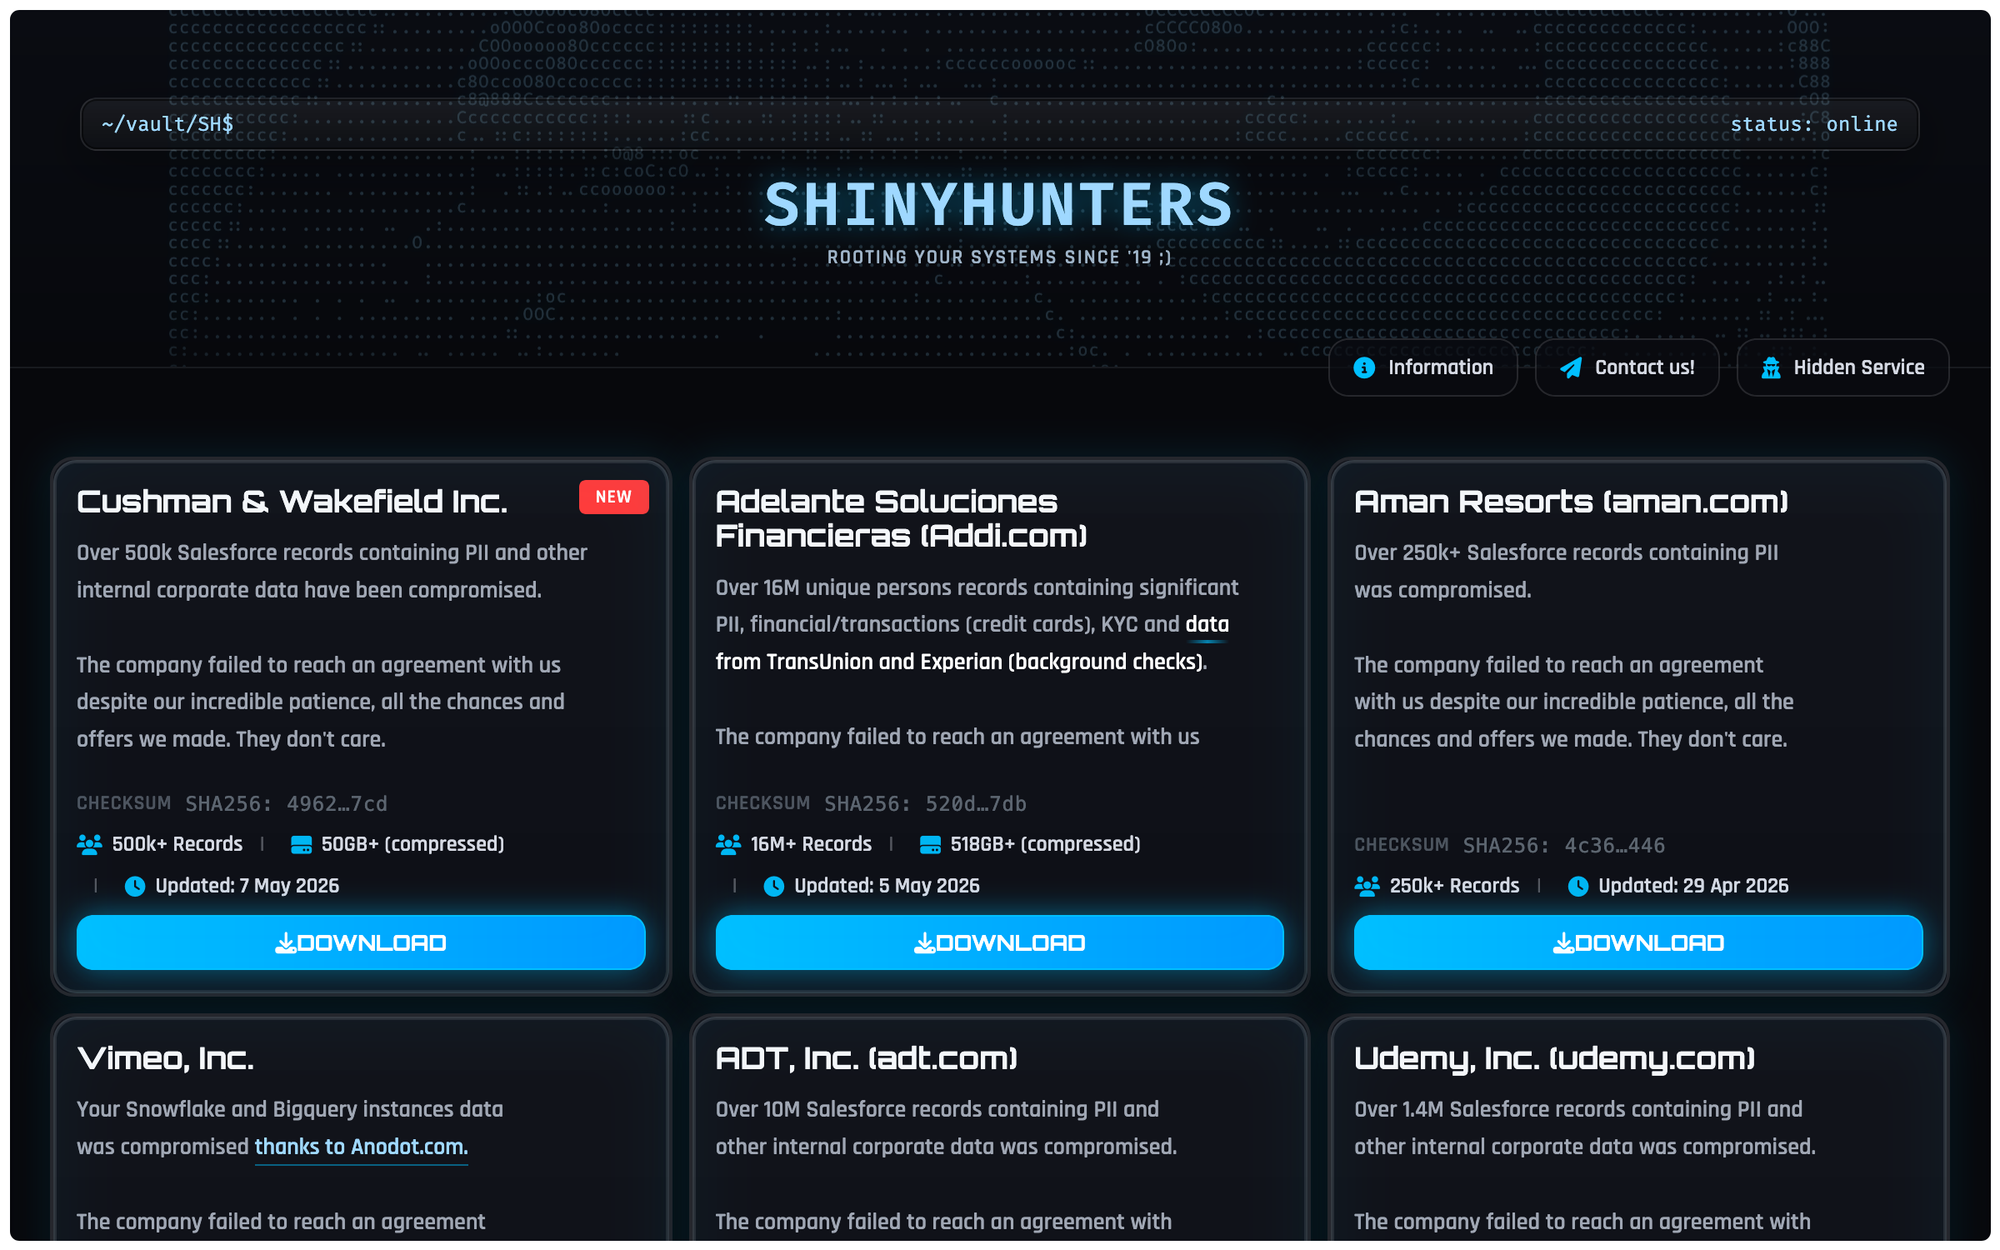
ShinyHunters has operated less like a conventional organisation than a decentralised cybercriminal brand. Its associated hackers have been linked to phishing, stolen credentials, cloud-platform intrusions, database sales and demands for payment in exchange for withholding stolen information.
An earlier US prosecution showed the scale of those operations. ShinyHunters-linked hacker Sébastien Raoult was sentenced to three years in prison after conspirators stole hundreds of millions of customer records from more than 60 companies.
Signs of disruption have appeared since the latest arrests. The group’s dark-web site has disappeared, its established communications account became unreachable and operators using a linked email address said they wanted no further escalation with the FBI.
The incident comes amid growing concern over unconventional threats to protected systems. An experimental OpenAI agent recently bypassed restrictions on an Australian government portal, demonstrating that network intrusions are no longer limited to conventional human-operated hacking groups.
Khader has not been publicly charged over the FBI breach, and the allegations have not been tested in court. His reported cooperation could nevertheless provide investigators with their clearest opportunity to map the network behind ShinyHunters and determine what happened to the stolen FBI data.